Security
Controls on every payout. No exceptions.
Moving digital assets is irreversible. Payrolloc is designed so that every payment is checked, approved and recorded before it leaves a wallet whichever custody model you choose.
01
Authenticated
The request comes from a permitted user or API key.
02
Validated
Addresses, assets, networks and amounts are checked.
03
Allowlisted
The destination is an approved beneficiary address.
04
Policy matched
Limits and rules for this payment are applied.
05
Approved
The required quorum has signed off.
06
Recorded
The full history is written to the audit log.
Security controls
Layered controls,
configured by you
Policy engine
Rules by amount, asset, network, destination, team or source wallet evaluated on every request.
Role-based access
Separate permissions to create, edit, approve, execute and view, scoped per workspace and wallet.
Separation of duties
The person who creates a payment cannot be the one who approves it.
Address allowlisting
Funds can only be sent to addresses approved on a beneficiary profile; changes require approval.
Spend limits
Caps per payout, per period and per wallet keep automation and people within agreed bounds.
Audit trail
Every login, edit, approval, rejection and execution recorded with user, time and context.
Strong authentication
Multi-factor authentication for users and scoped, revocable keys for API access.
Segregated wallets
Separate wallets per entity, team or purpose, each with its own permissions and policies.
Signed webhooks
Event payloads are signed so your systems can verify they came from Payrolloc.
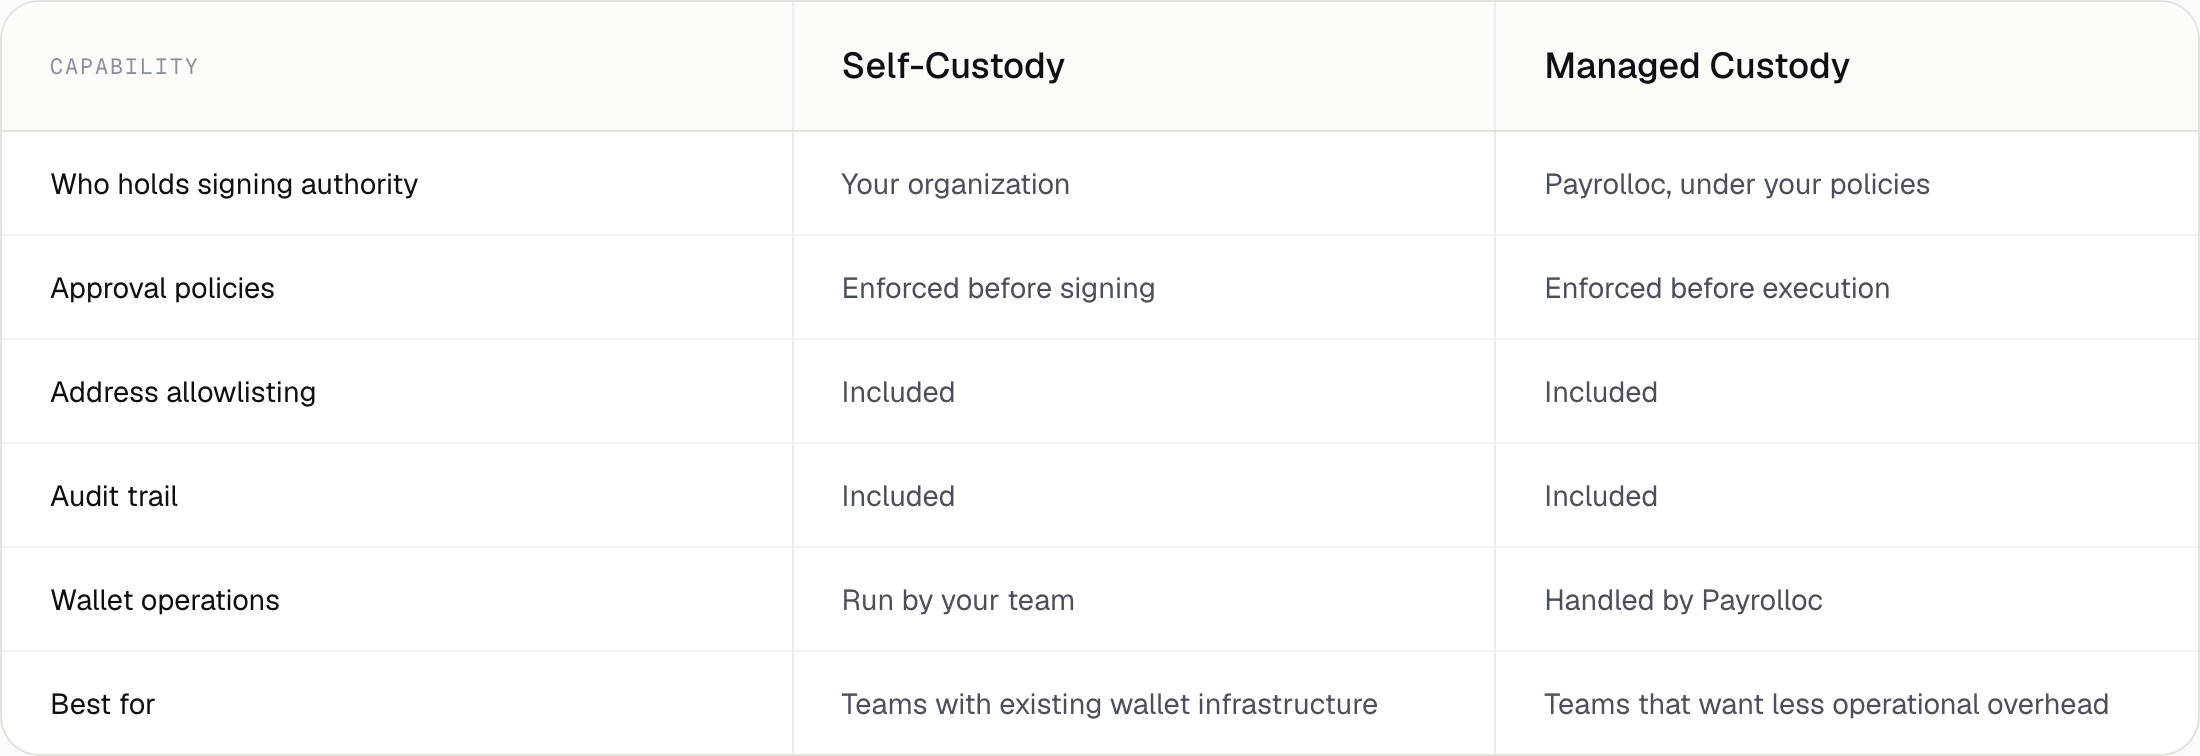
Custody models
Self-custody or managed.
Same governance.
Choose per wallet. Policies, approvals and audit logging apply identically across both.
Security reviews
Running a vendor assessment? Our team can walk your security and compliance stakeholders through Payrolloc's architecture and controls.
Responsible disclosure
If you believe you have found a vulnerability, please report it privately to security@payrolloc.com so we can investigate.
get started
Run your next
crypto payroll
with full control
See how Payrolloc automates, approves, executes and reconciles recurring crypto payments for your team.